As cyber threats grow more sophisticated and software supply chains become increasingly complex, public-sector organizations face mounting pressure to modernize their defenses. The 2026 edition of Securing the Cyber/Software Supply Chain will explore the strategies, technologies, and best practices for safeguarding the government supply chain and software assets.
Expert speakers from government and industry will share actionable insights and real-world approaches to securing mission-critical software infrastructure. Whether you’re responsible for procurement, IT security, or strategic planning, this workshop will equip you with the tools and foresight to stay ahead of emerging threats to the supply chain.
This year’s program will spotlight how agencies are:
Identifying and mitigating vulnerabilities across distributed software ecosystems
Strengthening vendor risk management and third-party assurance
Leveraging AI and continuous monitoring to detect anomalies and enforce governance
Navigating compliance with evolving standards like CMMC 2.0 and NIST SP 800-218
FEATURED SPEAKERS
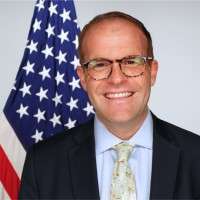
Nick Polk Branch Director, Federal Cybersecurity, Office of the Federal Chief Information Officer, OMB